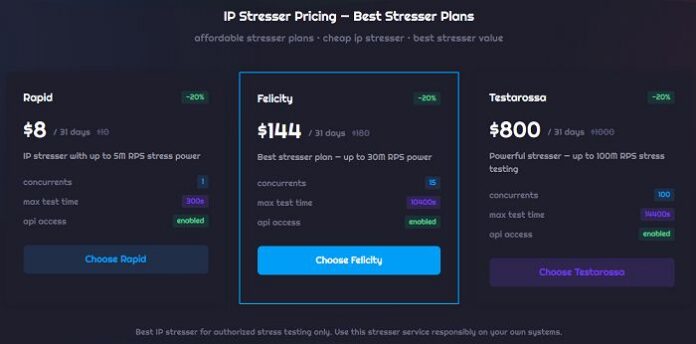

Brokered attacks are priced case by case, from USD30 to USD2,000, while DDoS-as-a-Service subscriptions can start at USD1
Kaspersky Digital Footprint Intelligence (DFI) reports that brokered DDoS attacks are priced on a case-by-case basis, ranging from USD30 to USD2,000. Prices vary with factors such as the target, attack duration, service limits, and available features.
WHAT THE RESEARCH LOOKED AT
In new research, Kaspersky Digital Footprint Intelligence experts examined how DDoS services are offered across the darknet, how different service models are priced and marketed, how competition shapes the market over time, and what behavioral patterns characterize the actors behind the supply.
They analyzed more than 256,000 DDoS-related posts across the dark and deep web and identified 148 DDoS actors active since at least 2024.
THREE ATTACK MODELS
Three main DDoS attack models stand out:
- Brokered attacks: A third party is hired to carry out the attack. Among observed brokered actors, 65 percent advertised on cybercriminal forums, while 35 percent used Telegram and Discord.
- DDoS-as-a-Service: Users buy a subscription to attack tools such as online control panels or Telegram bots.
- In-house infrastructure: Actors run their own attack scripts or botnets.
NETWORK-LAYER VS. APPLICATION-LAYER ATTACKS
DDoS activity centers on two attack types: network-layer attacks, which try to overwhelm infrastructure with heavy traffic, and application-layer attacks, which aim to disrupt websites and online services directly.
Kaspersky DFI analysis shows that 74 percent of actors advertised L4 techniques such as TCP (Transmission Control Protocol), UDP (User Datagram Protocol), and DNS (Domain Name System) floods, while only 9 percent explicitly referred to standalone L3 methods. L7 attacks were the most widely offered, appearing in 92 percent of cases, which points to both the broad availability of ready-made tools and the relative ease of targeting web-facing services.
“DDoS attacks have become a more practical and accessible option for threat actors, largely because these services are cheap and easy to obtain. In some cases, the cost of launching an attack can be lower than a standard monthly streaming subscription, or even for a price of a cup of coffee. For businesses, this means DDoS readiness should be part of basic cybersecurity planning. It is equally important to understand the market behind these attacks, since stronger defense begins with a clearer understanding of the threat environment,” said João Pedro Brandão e Silva, analyst at Kaspersky Digital Footprint Intelligence.
HOW ORGANIZATIONS CAN PROTECT THEMSELVES
Kaspersky recommends the following to strengthen business protection:
- Adopt a digital risk protection service that monitors an organization’s digital assets and detects threats across the surface, deep, and dark web, such as Kaspersky Digital Footprint Intelligence.
- Give InfoSec professionals in-depth visibility into cyberthreats targeting the organization. The latest Kaspersky Threat Intelligence provides context across the entire incident management cycle and helps identify cyber risks in a timely manner.
- Keep employees informed about relevant threats. The Kaspersky Automated Security Awareness Platform helps cultivate cyber-savvy behavior, including safe downloading practices.
- Augment existing security controls with human-led detection and global threat intelligence through solutions like Kaspersky Managed Detection and Response (MDR), which offers 24/7 monitoring, detection, investigation, and rapid response to sophisticated cyberattacks.